HIVE
my self-hosted proxmox and truenas setup: the hypervisor, mirrored storage, a vpn-gated download path and thirty-odd containers. it started in 2023 as a desktop running pi-hole and jellyfin, and i treat it as production, not just a lab.
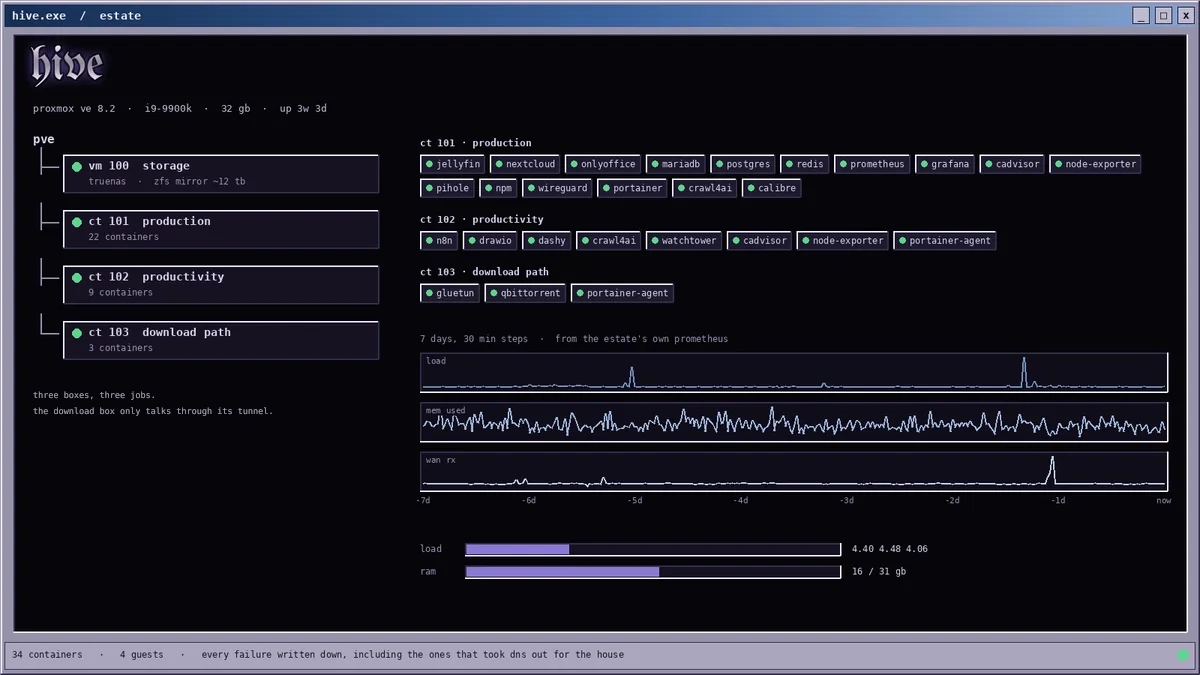
everything runs on one intel i9-9900k with 32 gb of ram and a mirrored zfs pool. proxmox runs the storage vm and three lxc containers, and i split those by how much i trust what’s in them: production services in one, productivity tools in another, and a download box whose traffic never leaves a vpn tunnel.
most of what i know about it came from it breaking. the dns filter also serves the rest of the house, so a bad config takes the internet down for people who never signed up for my experiments. storage lives in a vm, which means the host can finish booting before the disks it wants to mount exist, and every network share has to survive that. container networking also broke after an upgrade because a newer runtime changed how it writes to a namespace, so now there’s a written rule about which hosts get upgraded and which don’t.
the map here is the topology redrawn in this site’s style instead of exported from a diagram tool. one level down there’s a real compose file with the secrets taken out, and the retention policy that decides what survives a bad week.